PRODUCT: CYBERCRIME INVESTIGATIONS
UNCOVER THE ACTORS BEHIND CYBERCRIME FASTER
Investigate cybercrime, starting at the identity level
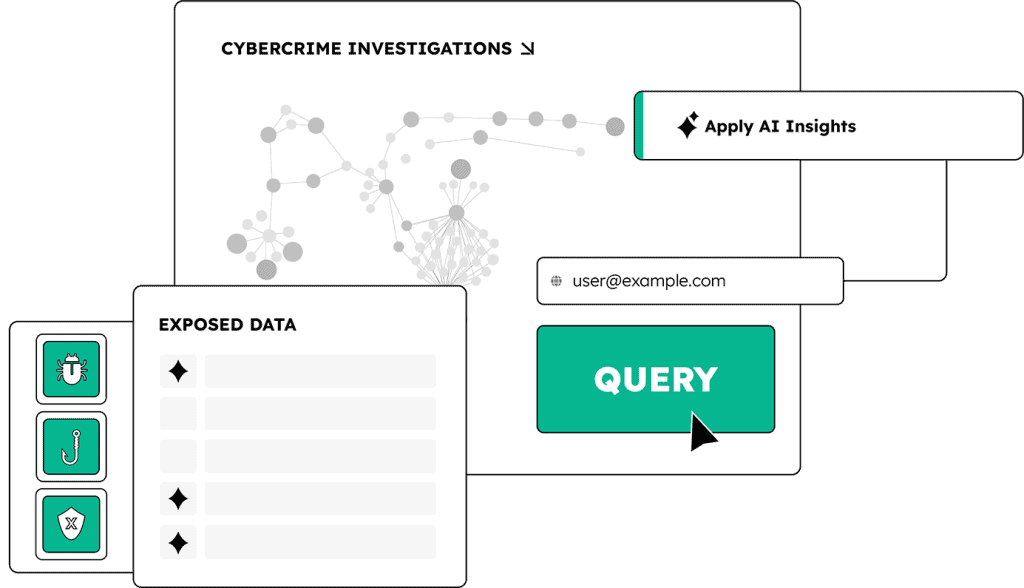
Cybercrime investigations stall when identity data is fragmented, incomplete, or buried in noise. SpyCloud Cybercrime Investigations brings identity to the center of your investigations, connecting breach, malware, and phishing exposures to reveal who’s involved, how they’re connected, and where to act next.
Start with a single selector – like an email address, username, phone number, domain, or IP – and pivot to uncover hidden relationships, alternate personas, and infrastructure tied to cybercrime activity.
With Research Agent, analysts can describe a subject, hypothesis, or batch of mixed assets in natural language and get a fully reasoned investigation plan, sequenced pivots, and finished intelligence in minutes, grounded in verified recaptured records. SpyCloud Investigations MCP extends these capabilities into analysts’ preferred AI environments, enabling natural-language queries and automated pivots.
Identity-centric investigations surface patterns of life and attribution signals that help analysts understand who’s behind the activity, not just what happened.
Explore powerful workflows & capabilities to aid your cybercrime investigations
Research Agent is essentially a natural language chat interface where an investigator can ask a question and basically say, tell me everything you have in the SpyCloud data for this selector. Customers can ask really more simple questions without that expertise, without mastering this domain, and get back much more mature, complete responses that would be what our investigator would get. It's all self contained, so it's not leaking out to the web. And basically, you can leverage that as though it's a partner throughout an investigation. It's not replacing the analyst because you still you still have to ask it questions, and you still have to pull the thread. We figure that the analysts and the investigators know exactly what they're looking for when they're conducting an investigation, but rather than have to hunt and peck through a lot of the data, you leverage the research agent by putting your thought of what you would be hunting for actually in a prompt, and basically they're saying, hey, research agent, go fetch this information for me. You can find signals in thousands, if not tens of thousands of records so much faster than it would take you to do it manually. I've got personal projects that I've worked on recently that last year would have taken me two months that I can accomplish the same thing now in a couple of hours. Scrambled email addresses, it'll tell you this is actually a phone number that's consistent with an area code in Indonesia. And, oh, by the way, here's the telecom provider. Whether they're looking at fraud, a threat actor, insider threats, all that's built into Research Agent. Because of that type of inferential prompting that was trained on, it gives you even that much more information. For example, it might be giving you a comparison of information, of exposure information, maybe give you some charts so you can better understand what you're looking at. It's closing the gap between what criminals are able to do and the amount of time that they have to profit from the data that they're stealing to when investigations teams can can stop it and prevent it from happening. It's leveling the playing field.
Let the Research Agent follow the leads
“SpyCloud is a cheat code – from one data point to the answer.”
– Senior Cyber Threat Researcher, Datadog
USE CASES
Cybercrime investigations powered by recaptured data
Built for analysts who need direct access to the world’s richest recaptured darknet dataset to use alone or alongside OSINT data sources. SpyCloud powers analyst workflows with the richest darknet data for cybercrime investigation and identity threat intelligence.
Threat Actor Attribution
Infected Host Identification
Financial Crimes Analysis
Supply Chain Exposure Analysis
Insider Risk Analysis
Identity Exposure Analysis
Synthetic Identity Analysis
Employment Fraud
Choose how you deploy SpyCloud Cybercrime Investigations
Same powerful intelligence. Three ways to put it to work.
- Investigate at the speed of the question – Start with a subject, hypothesis, or batch of assets. Research Agent builds an investigation plan, follows the evidence, and delivers findings grounded in verified recaptured records.
- Connect the identities. Expose the threats – IDLink automatically connects personal accounts, devices, aliases, and criminal personas to reveal relationships that manual searches might miss.
- Turn complex findings into actionable intelligence – AI Insights identifies suspicious patterns and attribution signals, helping analysts uncover what matters faster and deliver executive-ready reports in seconds.
- Natural language investigations with Research Agent
- Automated identity correlation with IDLink
- Full infostealer log access and AI-assisted Log Analysis
- Visual link analysis to uncover hidden connections
- AI Insights for pattern detection and attribution signals
- Executive-ready reports and raw log export for deeper analysis
- Start with an identity, question, or batch of assets
- IDLink connects related accounts, devices, aliases, and identities
- Research Agent builds an investigation plan, follows leads, and links findings to supporting records
- Visualize connections and explore new leads with interactive link analysis
- Examine infostealer logs and use Log Analysis to understand device-level exposures
- Use AI Insights to surface patterns and attribution signals and export findings
- Uncover stolen identity data – Query recaptured breach, malware, and phishing records to enrich investigations and reveal identity exposures.
- Connect identities automatically – Use IDLink to correlate accounts, aliases, devices, and personas, revealing relationships across seemingly unrelated data points.
- Investigate beyond stolen credentials – Access detailed infostealer logs, including cookies, autofills, browser history, and files, to understand the broader scope of device exposures.
- Query recaptured breach, malware, and phishing data across multiple identifiers
- Correlate connected identities with IDLink and retrieve structured identity graphs
- Retrieve parsed infostealer log data for deeper device-level investigations
- Connect to SpyCloud Investigations through a single API license
- Query breach data, identity connections, or infostealer logs as needed
- Combine SpyCloud results with internal and third-party intelligence
- Automate enrichment and analysis within your existing tools and workflows
- Investigate in natural language – Ask questions in your preferred AI assistant and let the agent select SpyCloud tools, run queries, and follow leads as evidence emerges.
- Connect evidence across datasets – Pivot between breach records, infostealer logs, identity connections, and exposure metrics to uncover relationships and accelerate investigations.
- Extend your AI security workflows – Combine SpyCloud's recaptured identity data with other MCP-enabled security tools for richer, multi-source investigations.
- 10+ tools across multiple SpyCloud datasets
- Multi-step querying and investigative pivots
- Identity correlation through IDLink
- Integration with supported AI assistants
- Access governed by existing SpyCloud permissions
- Connect your preferred supported AI assistant to SpyCloud Investigations MCP
- Ask a question using an identity, identifier, or hypothesis
- Your agent selects the appropriate SpyCloud tools and queries available data
- Follow new leads across breach records, infostealer logs, and identity connections
- Review findings and continue investigating in natural language
What analysts achieve with SpyCloud
"SpyCloud Investigations with IDLink has drastically reduced our investigation time, turning 2 hours of SOC work into just a few minutes."
SOC Manager, Global Airline
“SpyCloud Investigations delivers a level of comprehensive threat analysis that previously took our most experienced analysts hours to achieve.”
Vice President Of Global Security, Privacy and Compliance, Samsonite
"With SpyCloud Investigations, we have been able to uncover and address gaps we would have never known about in our suppliers' cybersecurity practices. Now we can enforce higher security standards across our entire supply chain."
Senior Director of Global Security & Privacy, Global Manufacturing and Retailer
EXPLORE MORE PRODUCTS
Know more, do less
Trusted by CTI, SOC, identity, and fraud & risk teams to expose hidden risk, accelerate investigations, and stop identity-based threats.
Workforce Threat Protection
Endpoint Threat Protection
Next steps
Pick a better starting place for your next investigation.
Request a demo today.
SpyCloud Cybercrime Investigations FAQs
SpyCloud Cybercrime Investigations is an AI-powered investigation platform built on the world’s largest recaptured identity corpus. Analysts and investigators at every skill level get direct access to over one trillion identity assets from infostealer malware logs, phishing kits, combolists, and breaches, with a layered set of capabilities designed to take teams from a single indicator to finished intelligence in minutes.
The investigation workflow moves through three layers. IDLink automatically correlates across the full digital identity, surfacing personal accounts, devices, aliases, credentials, and criminal personas without manual pivot steps. Research Agent (Pro) takes a question, a hypothesis, or a batch of mixed assets in natural language, plans the investigation, and runs the pivots across the data the way a senior analyst would, and returns finished intelligence grounded in verified recaptured records, with every finding traceable to a specific source. AI Insights (Pro) then applies decades of SpyCloud investigative tradecraft to detect behavioral patterns, surface attribution signals, and produce executive-ready reports in seconds.
The result: investigations that used to take hours now close in minutes, and every analyst on the team operates at the quality of your most experienced one.
The volume and complexity of OSINT data available to analysts and investigators makes it hard to quickly find the right information to remediate identity and supply chain exposures, mitigate insider threats, and complete cybercrime investigations. SpyCloud enriches your investigations with exclusive breach, phishing, and malware-sourced identity data; speeds up your workflows with automated IDLink pivoting; and improves your outcomes with high-confidence results.
After searching exact matches on an email, username, or phone number, IDLink automatically runs pivots in the background, looking for connections on everything that makes up a digital identity – from matching emails and backup emails, to shared and exposed PII, usernames, passwords, and over a dozen other asset types. SpyCloud Investigations with IDLink only returns new, highly-relevant results, removing any out-of-scope identity asset that slows down analysis. It also enhances raw data with additional context to give you a broader view of exposed identities and threats.
No. The intuitive interface and automated workflows are designed for analysts at all levels.
Yes. SpyCloud cross-references all data sources – from breaches, malware logs, and phishing campaigns – to uncover hidden relationships across identities and assets.