

As the autumn leaves are falling around us, the SpyCloud Labs team has been staying cozy, drinking pumpkin spice lattes, and watching out for new developments in the cybercrime underground.
This month’s update covers:
- ShinyHunters’ threats against Cl0p and the FBI,
- The arrests of two prolific ShinyHunters hackers in two different countries,
- More updates in the Forum Wars, including some policy changes on PwnForums,
- An interesting infostealer log showing business ties of Oxygen Forensics.
Let’s get into it!
ShinyHunters fights with Cl0p and the FBI
In September, SLSH – a data-theft extortion gang named after three other hacking groups: Scattered Spider, LAPSUS$ and ShinyHunters – started fights with both the prolific Russian-speaking ransomware group Cl0p and the FBI itself. Beginning on September 19, the Cl0p DLS onion domain appeared to have been hijacked and was rendering the content for the SLSH DLS. Over the next few days, the SLSH data leak site (DLS), which now could also be viewed via the Cl0p DLS domain at times, was updated with an escalating series of threats against Cl0p:
- September 19 SLSH Post: Note to Cl0p-_-
IF YOU WANT TO SAVE YOUR BRAND AND NOT DIE BY MY HANDS: Email us from your official email at shinygroup@onionmail.com and lets see how rich you really are. 2.333% of my networth is a 8 figure amount, I hope you can pay that much because that is the demand, negotiable. Get your bosses in front of the white board in the war room. Clock is ticking moron. Kindly excuse our unprofessionalism.
- September 20 SLSH Post Update:
Dear Likhogray & Tarasov, tell your boss j0nny to wake the fuck up. Run those pockets. I want all the money you made off the EBS campaign plus more AND WITH INTEREST. before I start releasing information regarding the companies that paid you, how much, and to what Bitcoin address. My phone book contains all major financial media outlets. CLOCK IS TICKING! LETS GET THE BALL ROLLING! Be sure to bring an English interlocutor so you can comprehend my literacy in acquiring your bank account. 66 hours remaining.
- September 21 SLSH Post Update:
Every 24 hours you fail to engage with us the demands increase. The demand now includes a mandatory apology issued directly to me PUBLICLY. I am 3-0 against you rich and broke criminals.
- Late September 21 Cl0p Update:
Cl0p posted a single HTML message to their original DLS which read, “Shiny Hunters we trying to reach you Your email does not work. Come online old platform no email.”
- September 22 SLSH Post Update:
RESPONSE: Its spelt *ShinyHunters, with no space, moron. I told you to bring an English interlocutor. You’re a rat. You attempted to intimidate me by saying you’ll hand me over to the police. You contact me on my terms, not the other way around. I don’t have access to old platform anymore. Did you forget how extortion works? You’re being EXTORTED.
Another 24 hours passed. The new demands now include: Make sure to have MY money in Bitcoins, traceable, linked to your previous activity, ready so the whole world can see that I walk all over you and your other Russian buddies. Qilin cocksucker. Maybe go ask Big Boss Qilin Haise for a loan if you don’t have the money after spending it all on them crack whores and WEAK zday exploits. Atleast I can make my zdays instead of buying them.
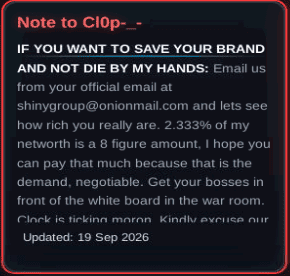
Initial Cl0p threat posted to the SLSH DLS.
As these escalating threats were transpiring, both the SLSH and Cl0p sites had connectivity and download issues for both DLS and file servers, likely due to both groups attacking each other’s infrastructure. Later on September 22, all of these Cl0p posts had been taken down, replaced by a new series of threats and demands for the FBI, including a claim that they had breached sensitive FBI personnel data. The group also put out an open call to journalists, promising to send them a sample of the breached data, and multiple outlets confirmed the veracity of the sample data.
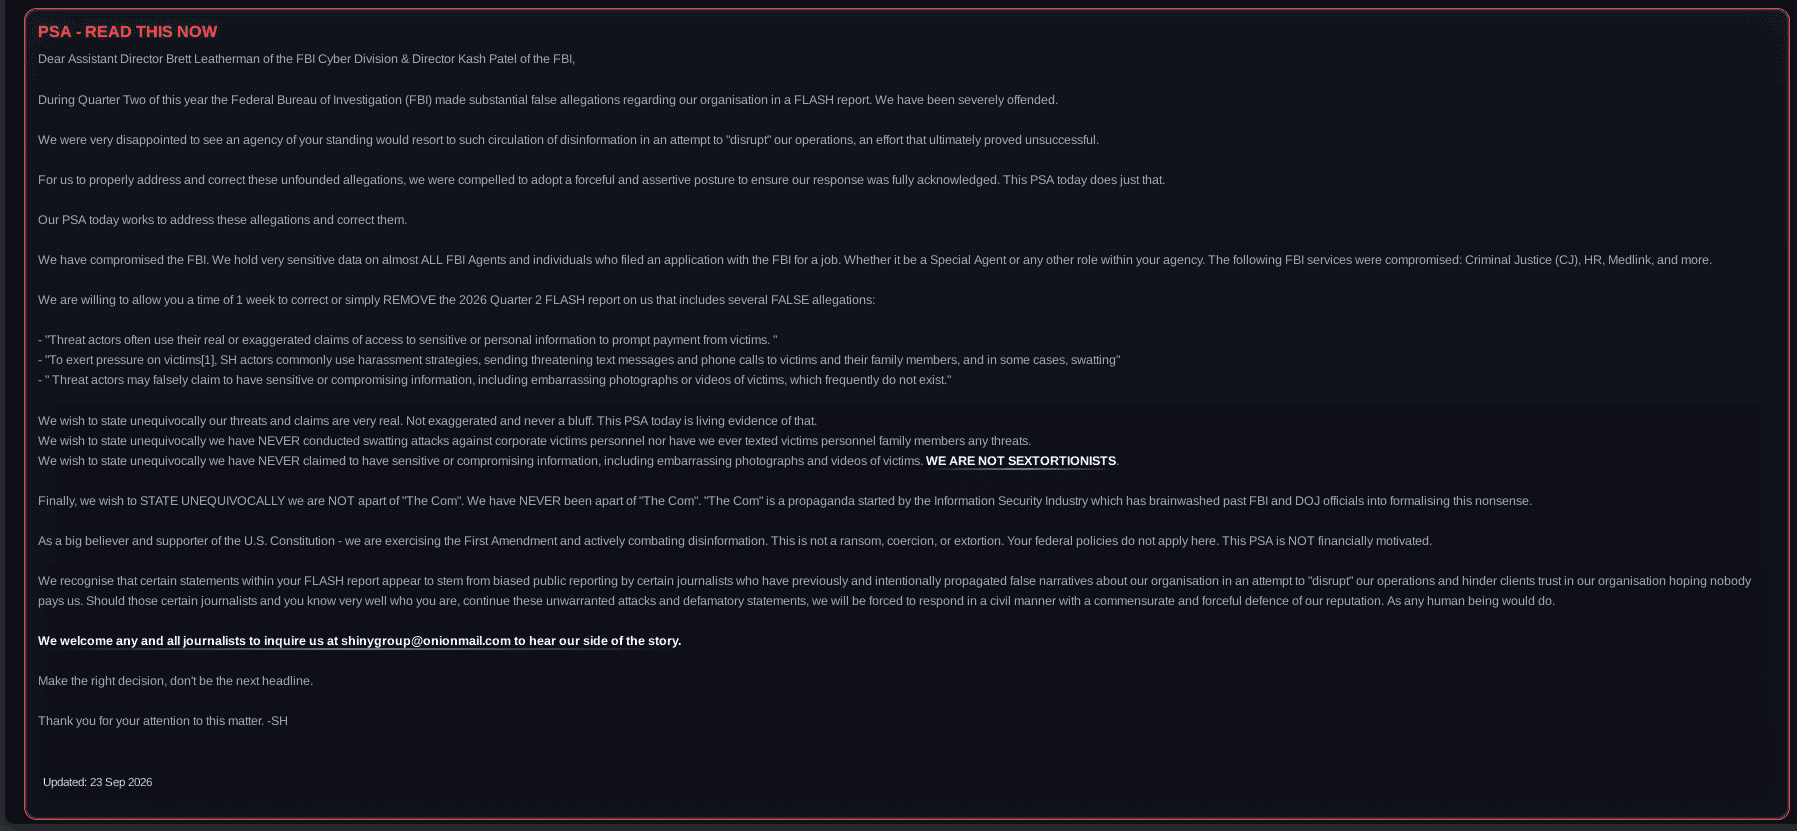
Threat against the FBI from the SLSH website, originally posted September 22.
During this flurry of activity, law enforcement authorities also arrested two SLSH-affiliated actors; the individual behind the moniker Umbreon was arrested in the Netherlands and Rey was arrested in Jordan. In addition to a host of cybercriminal charges, Pepijn van der Stap – the real person behind Umbreon – is being charged with the attempted incitement of two murders. KrebsOnSecurity reported that van der Stap’s arrest was on September 16, and Reuters reported that Saif al-Din Khader (the real identity of Rey) was arrested on September 29. This means that the brazen public threats, hacking, and hijacking carried out against Cl0p and the FBI occurred in the window between these two arrests.¹
As of the time of this writing, the original SLSH site appears to be offline. There is a new site that is up but so far it is unclear whether this new site is just a clone from cached data run by scammers or if it is indeed SLSH trying to reappear after losing Rey. Currently no new listings of victims have been created and all previous in-process victims have been removed.
¹ Technically, the compromise of the FBIJobs.gov portal by ShinyHunters, which allowed them to steal FBI personnel data, may have occurred prior to September 2026. However, the public announcement of this theft and associated threats all occurred in mid-September. ShinyHunters obtained this data by exploiting a vulnerability in Oracle’s PeopleSoft software, and ShinyHunters had been observed exploiting that PeopleSoft vulnerability in the wild as early as May 2026.
Forum Wars dispatch: PwnForums is tightening the ship and RAMP is back?
PwnForums – one of the more popular English-language data breach forums – appears to be tightening their controls on users who want to create and maintain accounts on their forum. On October 1, the Admin account on the forum made an announcement updating their forum participation and moderation policies to cut down on behavior they deem as “leeching”. They then point to an example of a rule they wish to more strictly enforce: a requirement that leaks posted for sale in the Marketplace category must include sufficiently large free data samples (e.g., “leaks containing more than 50,000 unique lines must include at least 1,000 unique lines as samples”).
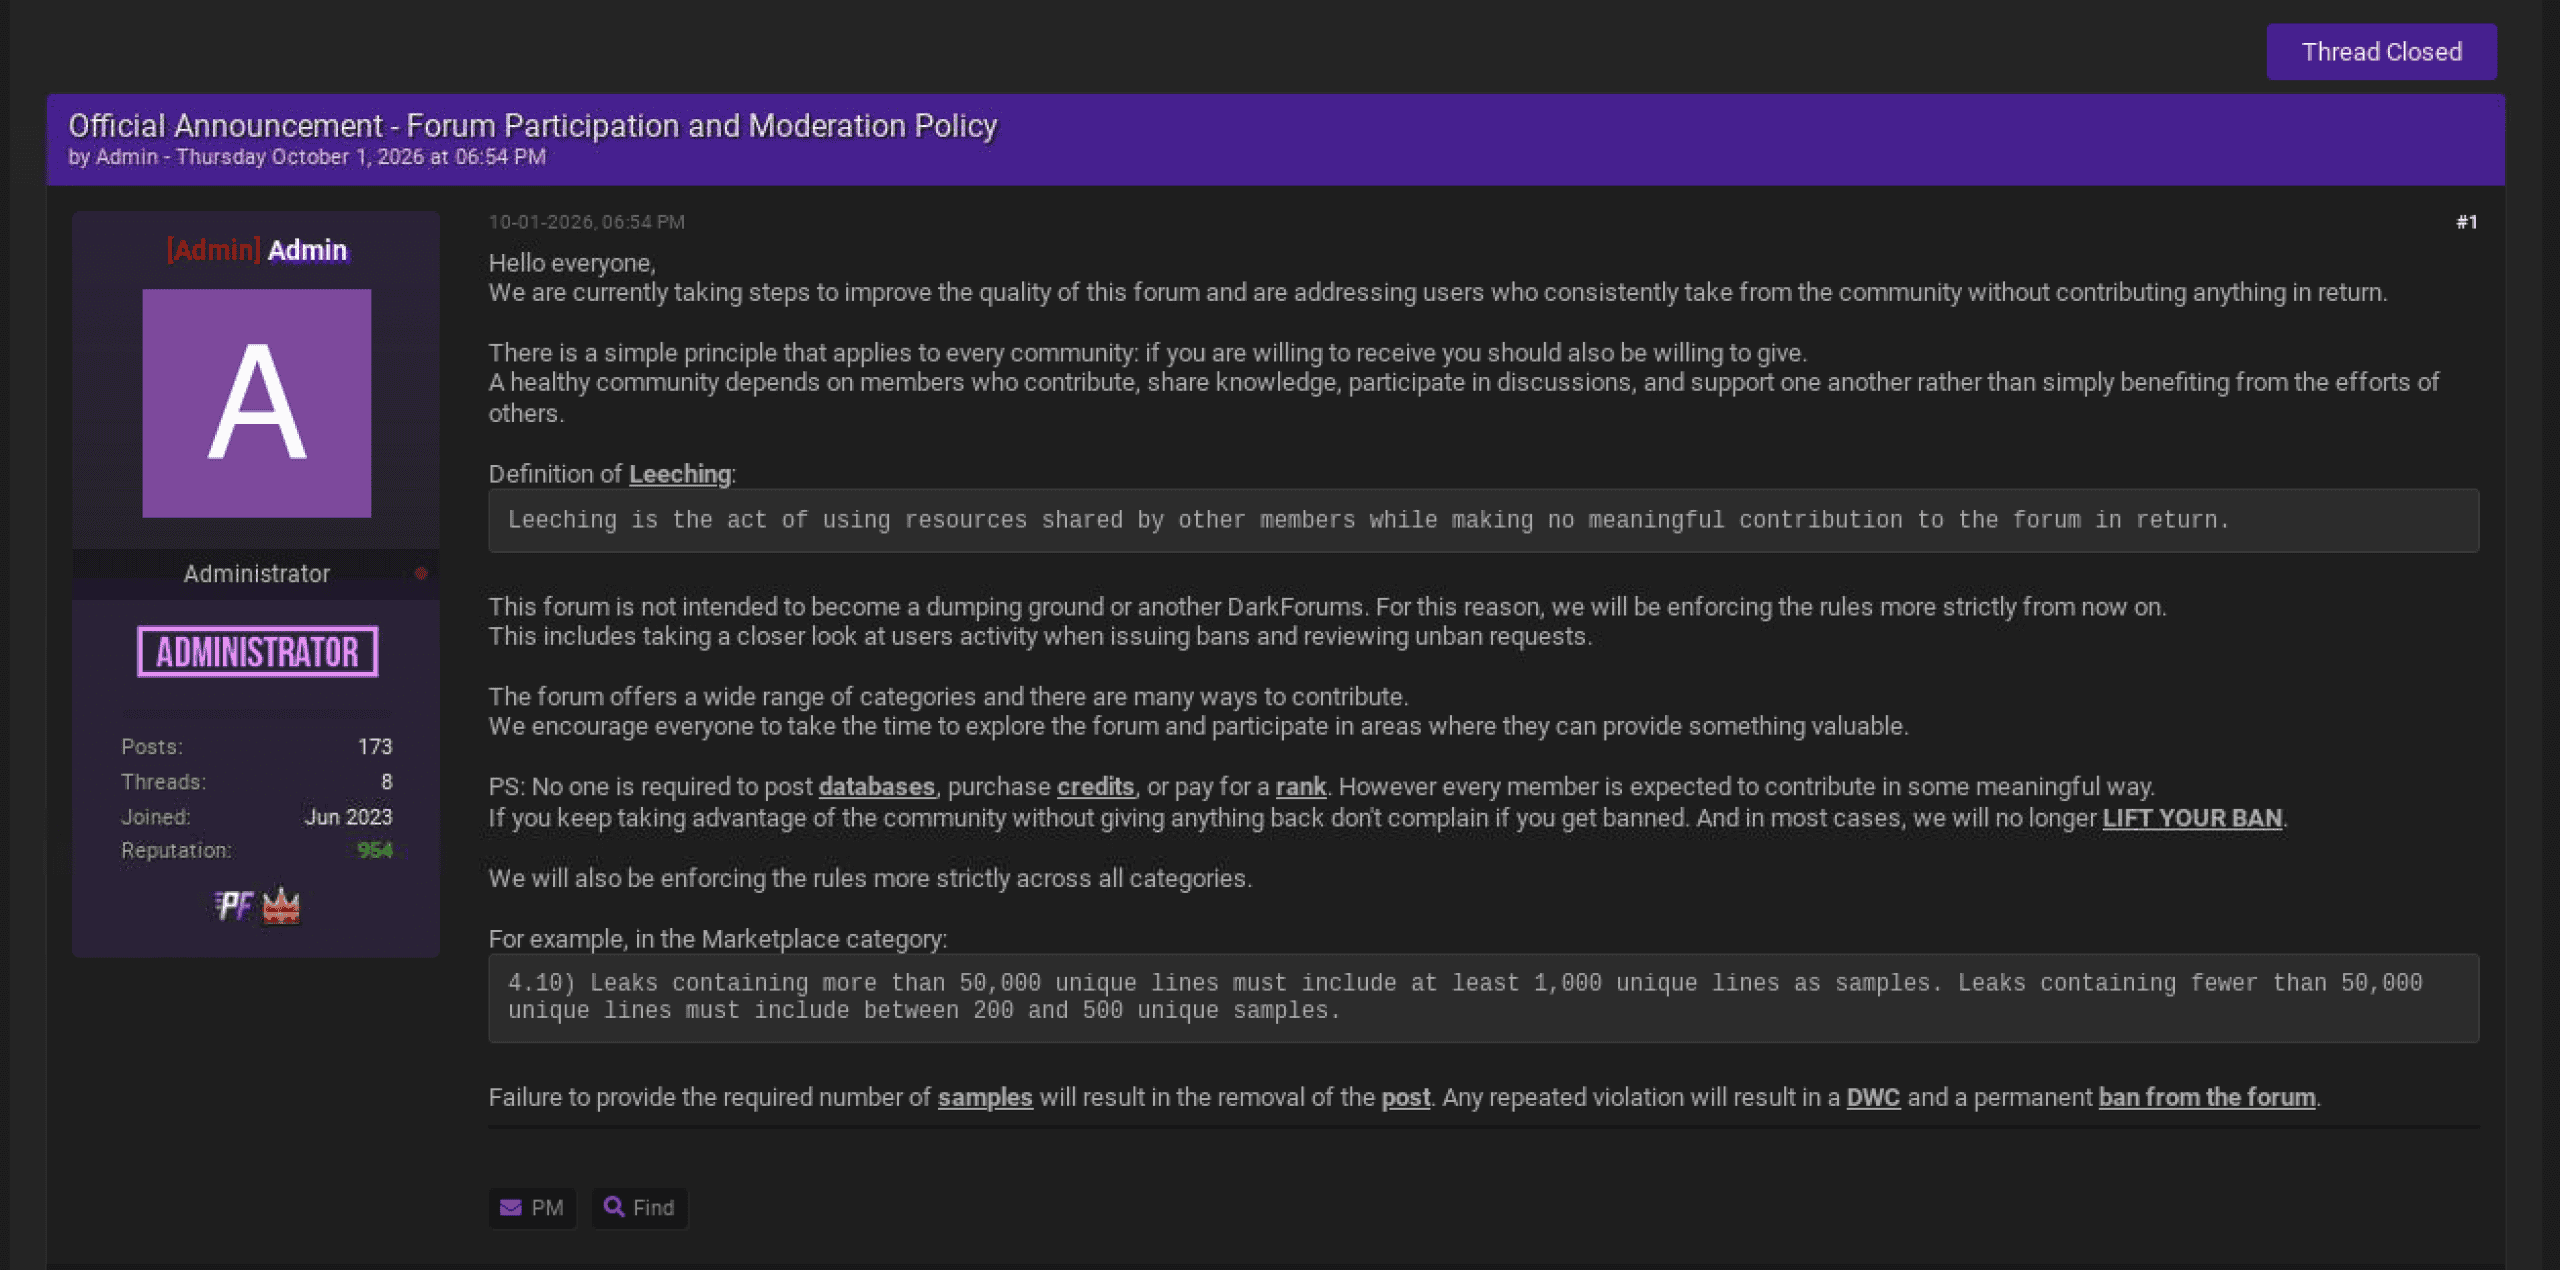
PwnForums post detailing their new “Forum Participation and Moderation Policy”.
This vow of stricter moderation comes in addition to already existing account activation requirements, including both an email verification check and a Proof-of-Work verification required for all newly registered accounts. A Proof-of-Work (PoW) verification is a type of cryptographic proof that verifies a certain amount of computational resources have been expended. PoW first emerged as an anti-spam mechanism, but was made most famous by its role in the consensus mechanism of cryptocurrency blockchains – cryptocurrency miners compete to solve PoW challenges on the blockchain and the solutions must be agreed upon by all nodes to reach a consensus, thus confirming each new transaction.
PwnForums also has an “automatic refund” mechanism – a carryover from the time period when the site that would become PwnForums was a BreachForums copycat site. This feature is also intended to cut down on leeching behavior; it allows users to recoup their credits if, after they pay to unlock the hidden content of a post, the hidden links end up being dead (usually because the filehosting site they have uploaded the data to is unresponsive or has taken the content down). The “automatic” adjective is a bit of a misnomer here; the process is not instantaneous and still requires a moderator to review your request to process the credit refund.
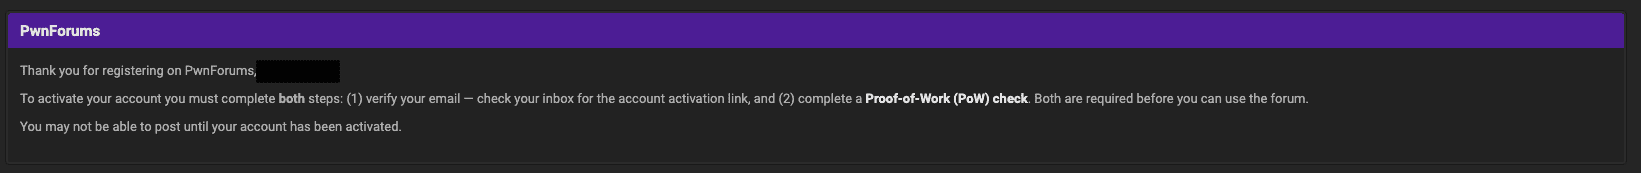
PwnForums requirements to activate an account after registering, including an email verification and a Proof-of-Work verification.
Back in May, PwnForums also introduced a new ban on any activities targeting Russia and other CIS countries. This is common for Russian-language forums and Russian threat actors, who generally enjoy impunity for their cybercrimes as long as they do not target CIS persons. However, it was unclear what drove this decision for PwnForums – perhaps it was driven by a Russian infrastructure provider or admin, or by a desire to be a more appealing gathering place for Russian users.
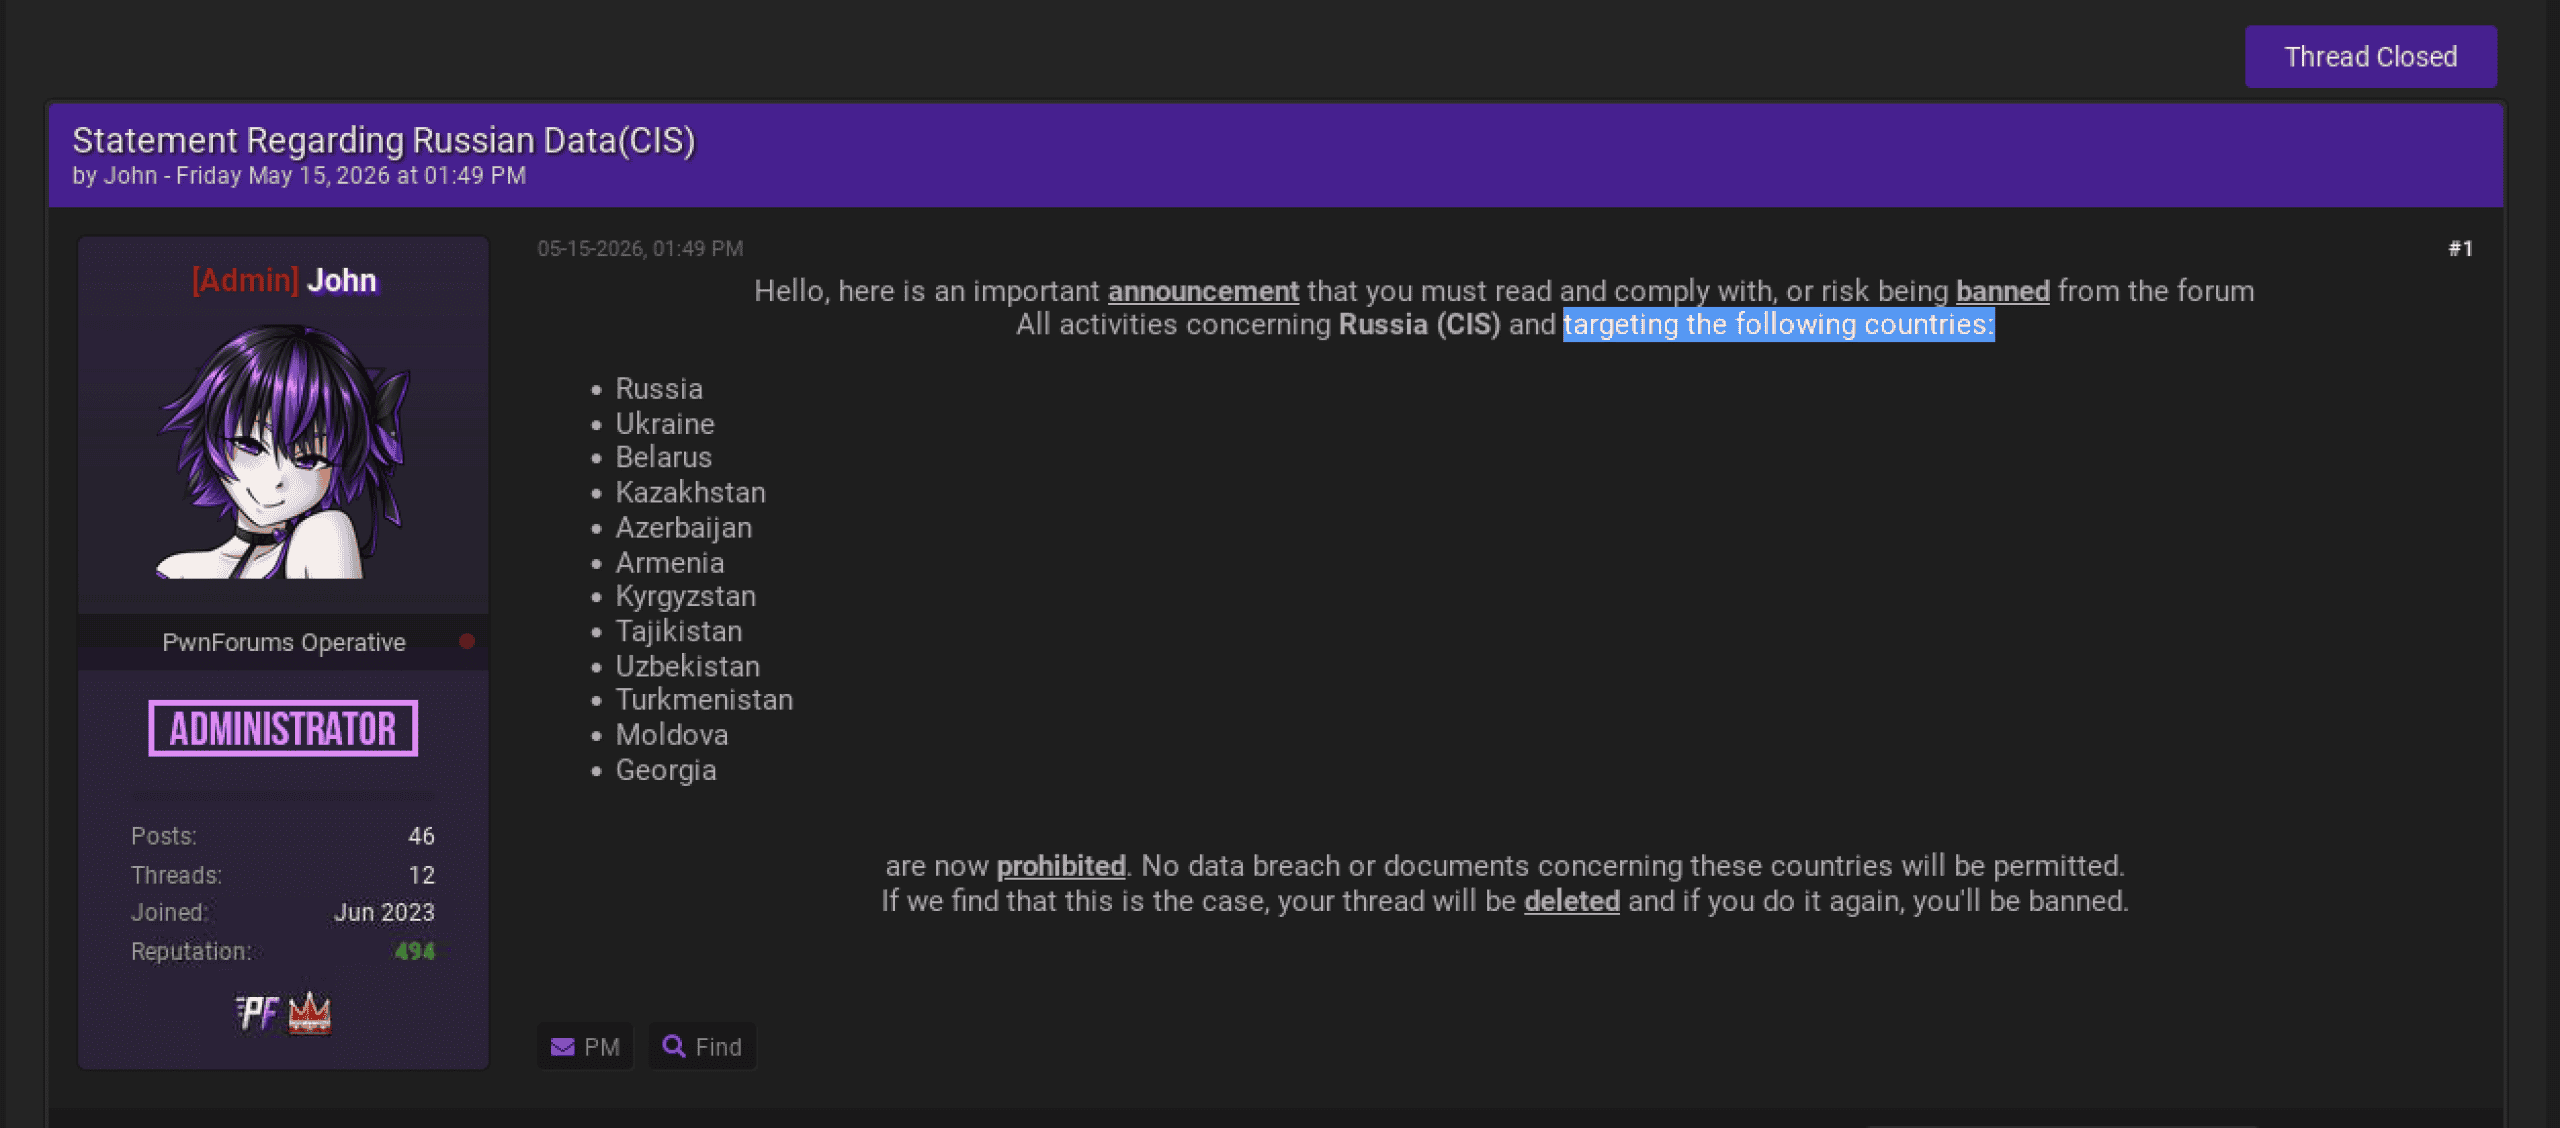
PwnForums announcement banning content from Russia and other CIS countries, posted on May 15, 2026.
RAMP, a Russian-language criminal forum popular with ransomware actors, was taken down back in January. This month, we noticed a new RAMP site pop up, with the domain names ramp4u[.]com and ramp4u[.]net (both very similar to the original site’s ramp4u[.]io domain). However, while this new site looks similar to the old RAMP, old credentials for the site do not appear to work on the new site – indicating that the creators of this site don’t have access to data from the old RAMP’s backend. Registration for new accounts on this site costs $500 USD paid up front via cryptocurrency, and there are apparently no options to register a new account for free. A database with backend user data for RAMP (allegedly stolen back in early 2024) actually recently leaked on PwnForums in early August. This makes it even more suspicious that there are apparently no options to recover old accounts, as many new criminal forums trying to emulate old forums will import user tables from those old forums, even when they aren’t being run by the same group of actors.
The fact that old accounts don’t work on this new site, the $500 flat fee for any new account creation, and the general lack of buzz about this new RAMP site in cybercriminal chats and forums that we monitor all make us somewhat suspicious of this new RAMP revival. We will continue to watch this new site, but as of right now, we suspect that this very well might be an exit scam.
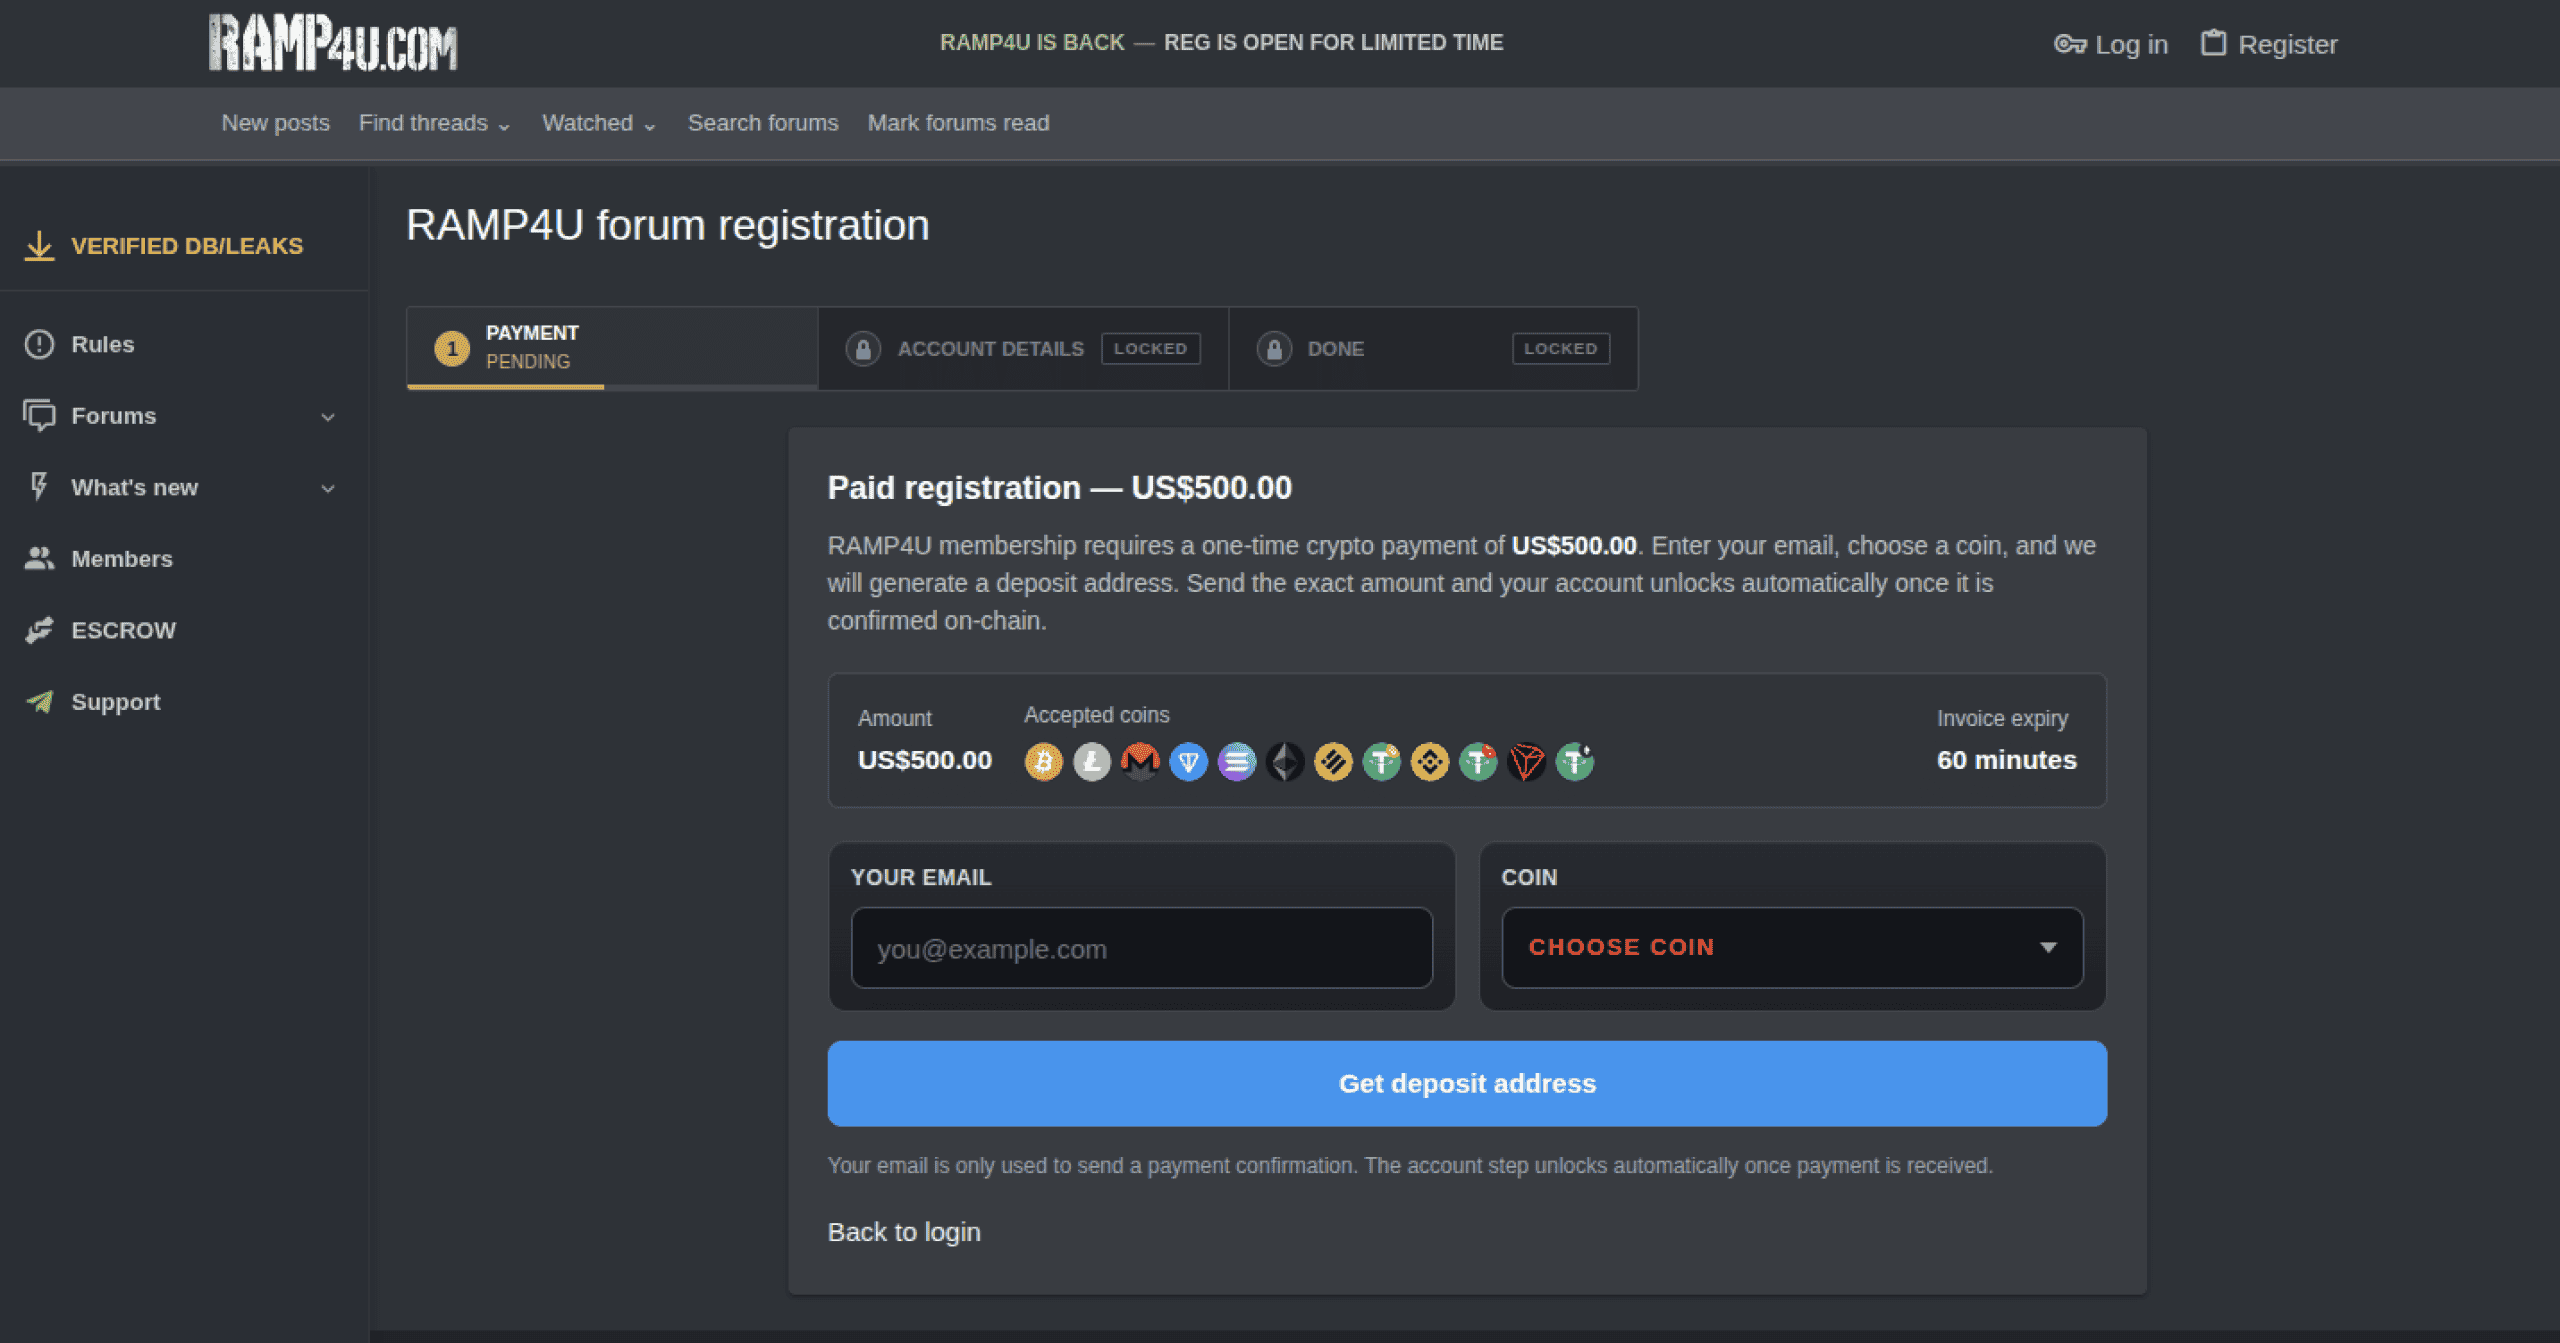
Account registration page for ramp4u[.]net charging $500 to create a new account.
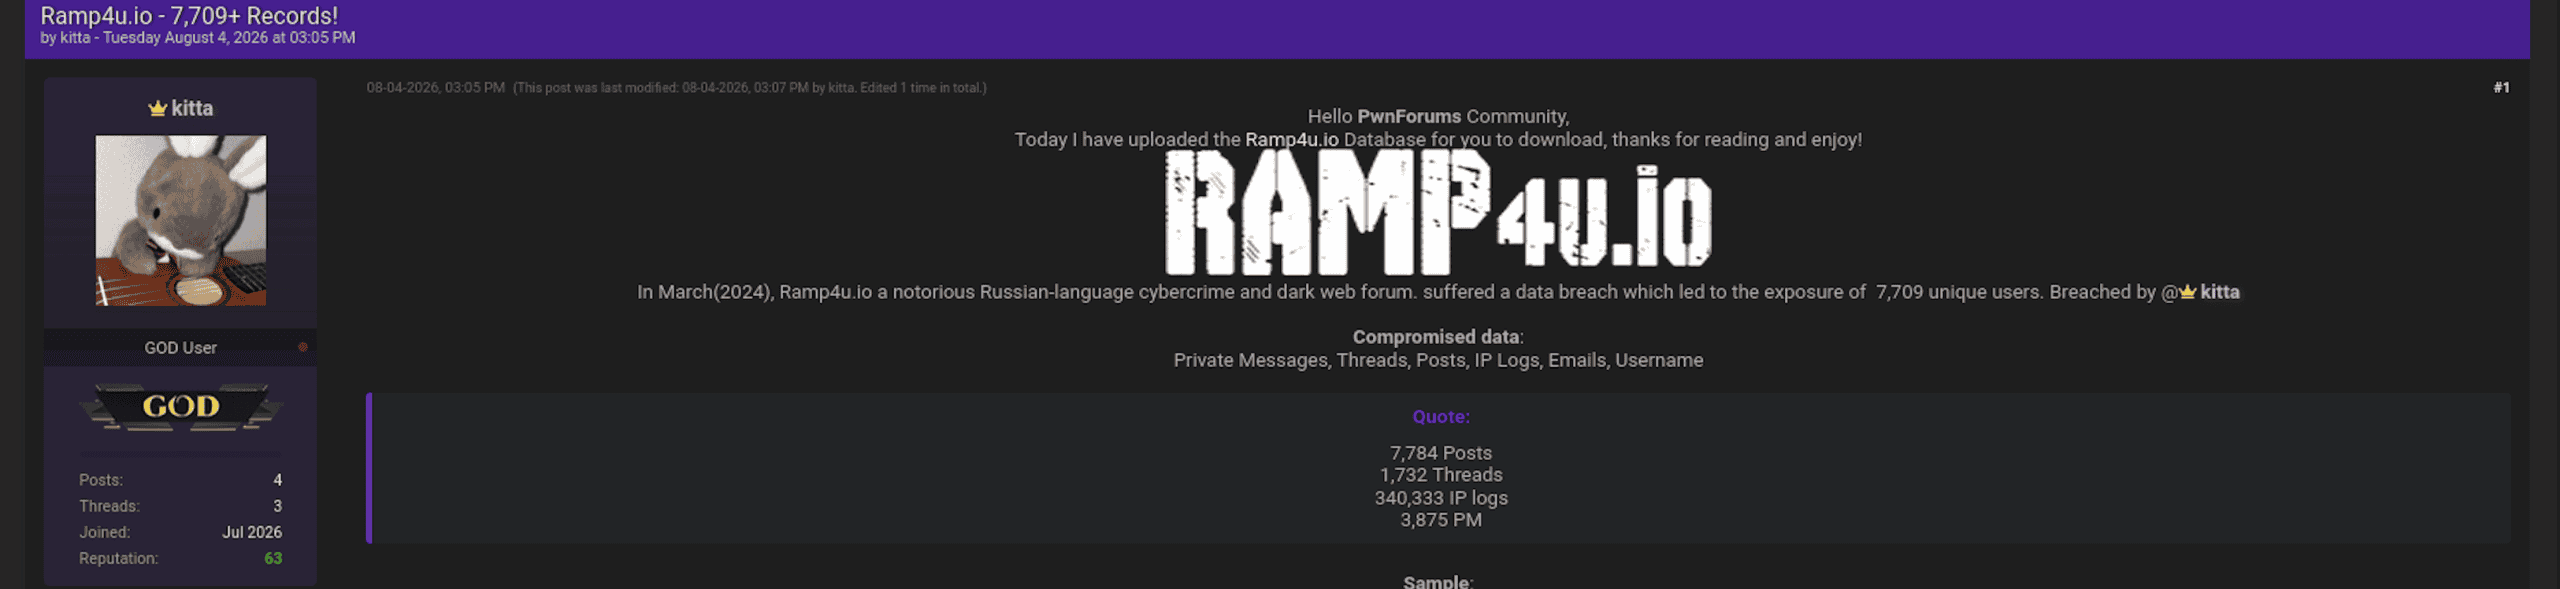
RAMP user database leak posted to PwnForums.
Charges against Oxygen Forensics for concealing their Russian ownership
Oxygen Forensics, a mobile forensics company that provided data extraction tools to American law enforcement organizations, was discovered to have Russian ownership. That firm actually provided the same mobile phone unlocking tools to both ICE (USA) and the FSB (Russia). Both the company’s American CEO and its Russian CTO (a Russian national who co-founded the company) were arrested on Sunday, September 20, on charges of conspiracy to commit wire fraud.
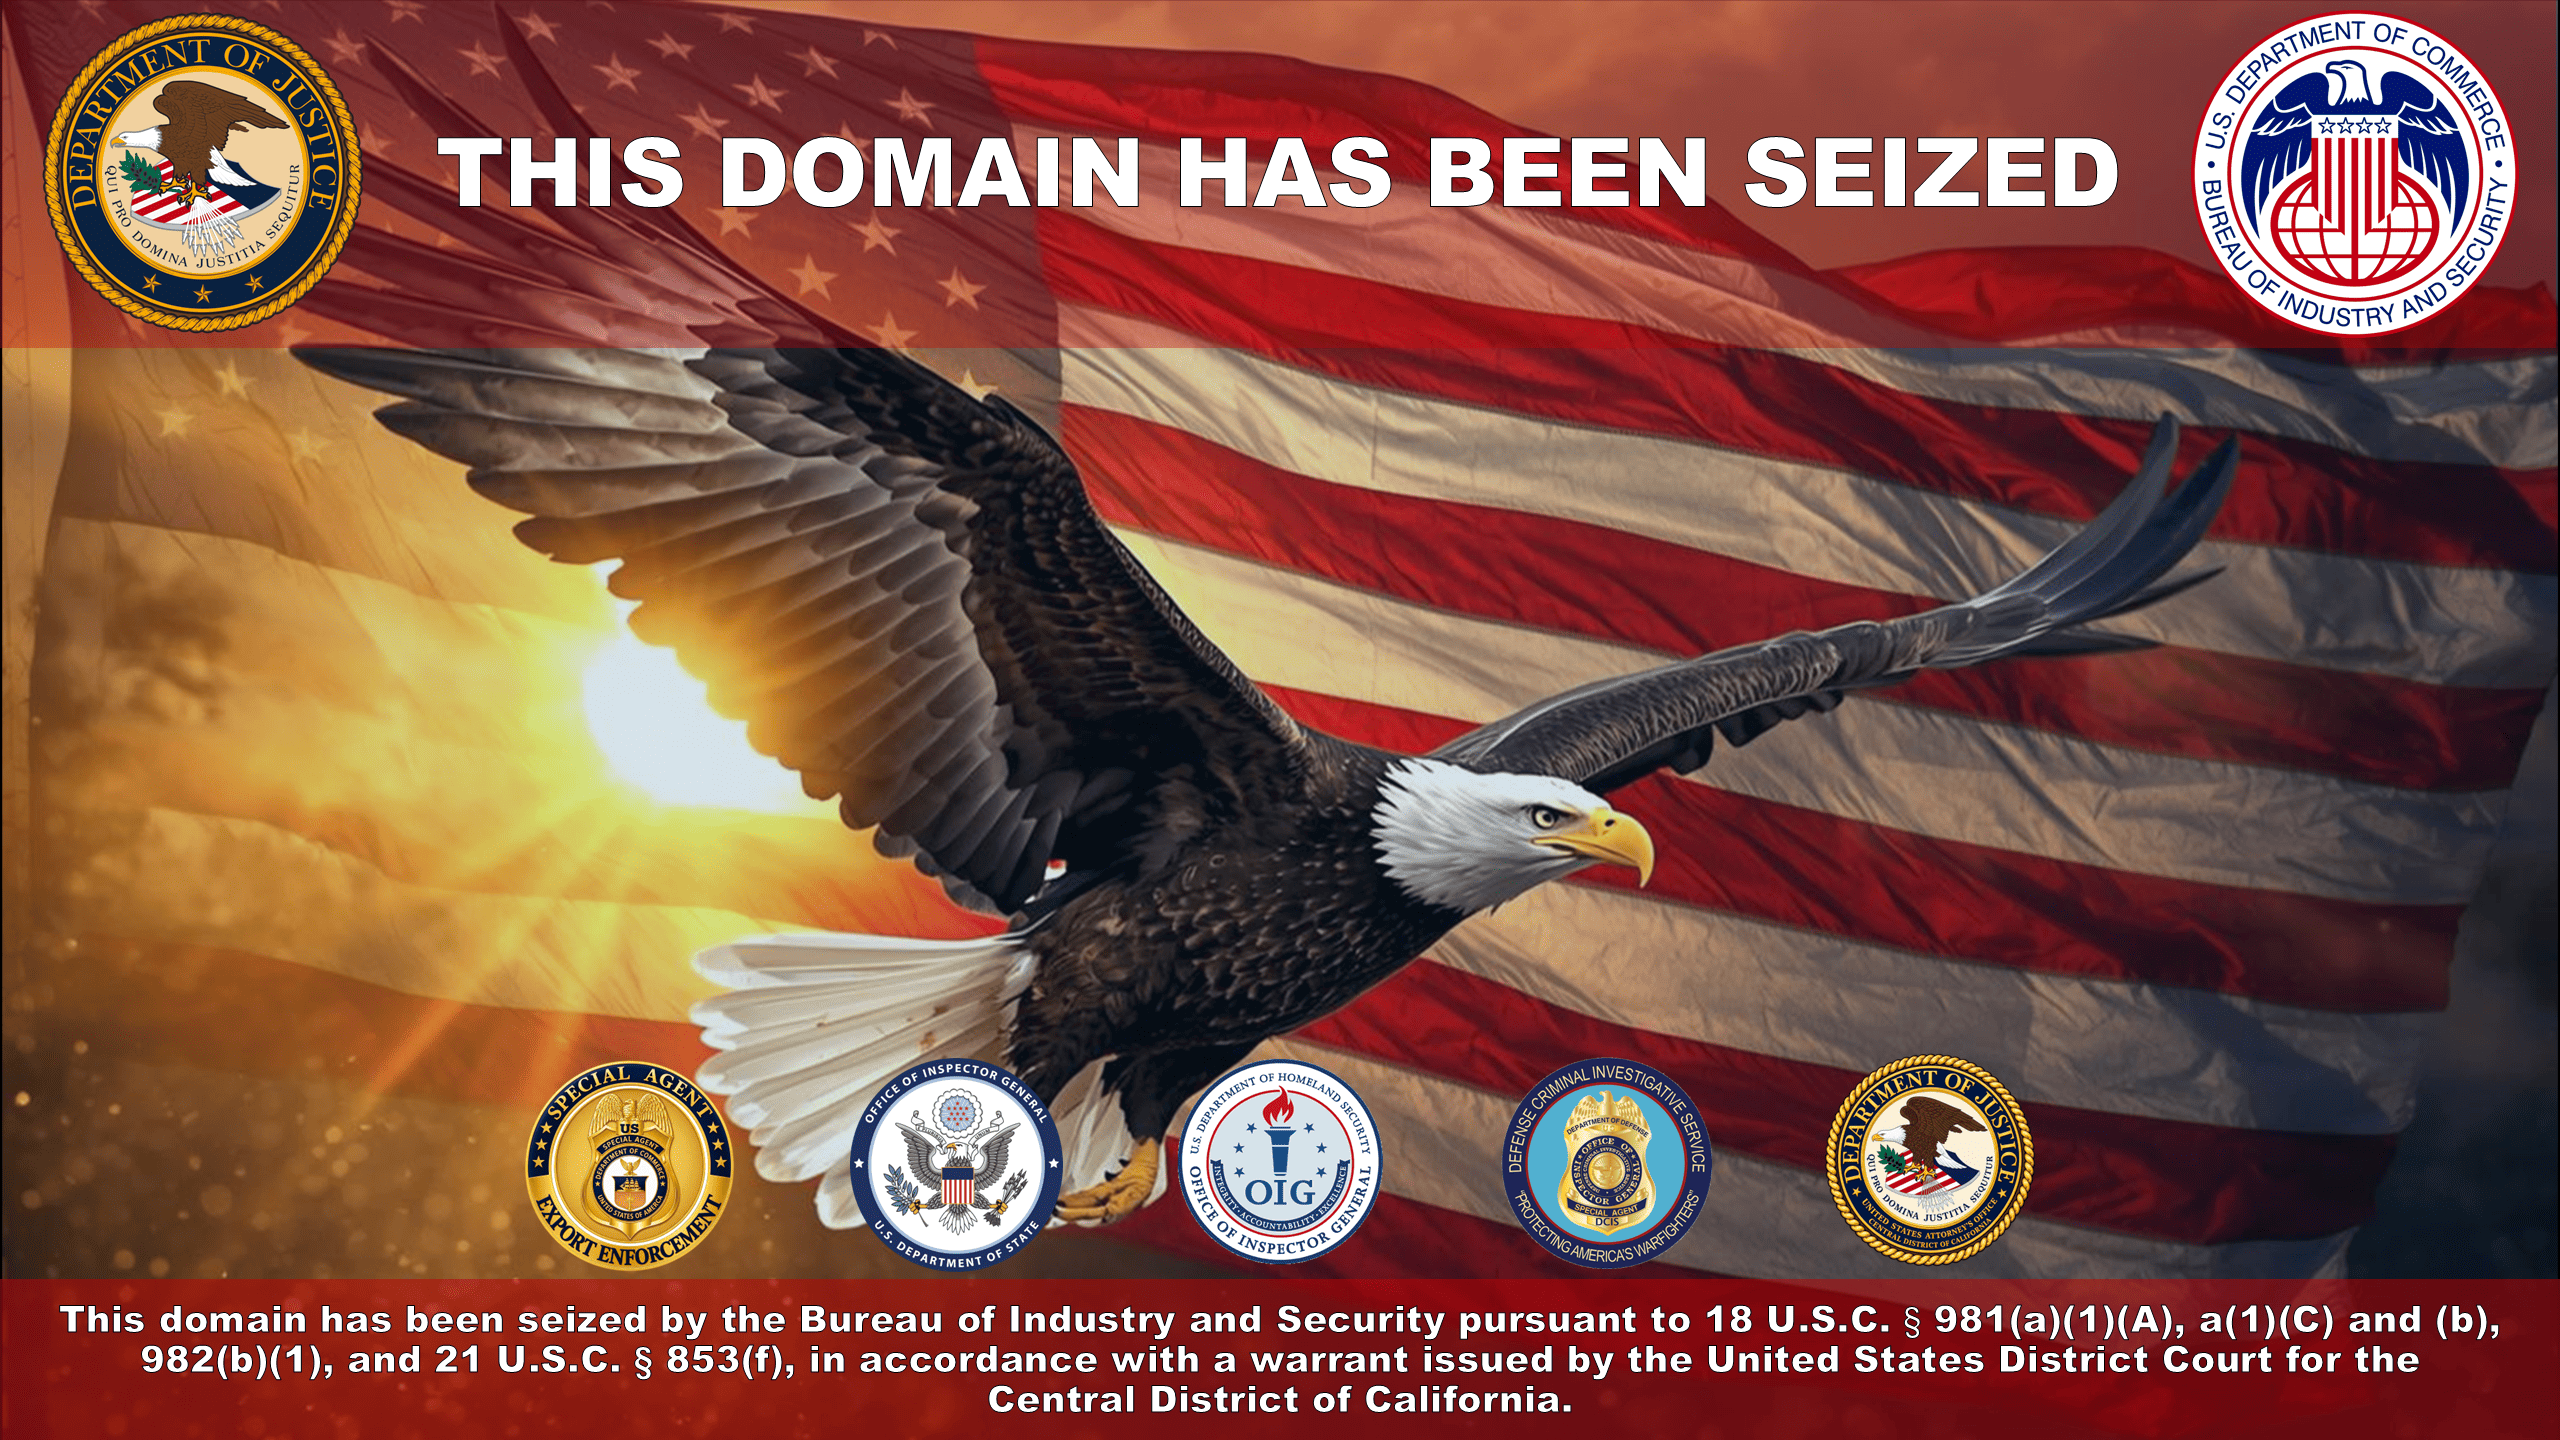
Current state of oxygenforensics[.]com.
Analysis of infostealer log data in the SpyCloud Investigations API also reveals additional connections with other authoritarian government powers, such as those in Guatemala. For example, one user had an account at partners[.]oxygenforensics[.]com, but their email belonged to grupoitd[.]com, a Guatemalan forensics outfit – implying a partnership between Oxygen Forensics and Grupo ITD. Coincidentally, authoritarian-aligned Guatemalan politician Maria Porros, whom OCCRP named the “2023 Person of the Year in Organized Crime and Corruption”, served as the Guatemalan Attorney General up until May of 2025, and in April of 2025, her office attempted to acquire the Grupo ITD’s capabilities for data extraction. The contract was canceled shortly after, with Porros stating that the contract was “inconvenient for the interests of the institution and due to a lack of consistency in the aforementioned documents, the Public Ministry is not certain regarding the condition of compliance with the guarantee requirement,” a rather evasive statement suggesting a compliance issue.
Pivoting on the oxygenforensics[.]com domain via infrastructure analysis shows several similarly-named domains, and one similarly-themed domain, including forensicsuite[.]com, oxygen-forensic[.]com, and oxygen-forensics[.]com. Recaptured infostealer logs associated with these domains suggest that Lebanon’s military and border enforcement were utilizing the company’s services at [specify domain], spanning 2019-2023.
Further pivots off of these domains revealed yet another domain, oxygensoftware[.]com, registered 2000-01-25. Pivots off of this domain in the Investigations API return Oleg Davydov – the arrested Russian national – and his passwords, as well as an account on GSMHosting, a phone hacking forum. This data going 26 years back matches the now-public story of Oxygen Forensics: Oleg is a true founder of Oxygen Forensics, and his Virginian counterpart was simply installed as CEO in 2022 in light of increasing sanctions on Russia.
Other research insights from SpyCloud Labs
SpyCloud Labs data shows StealC fell 90% before the June 24 Operation Endgame takedown. See what our post-takedown analysis reveals.
EvilTokens, a top PhaaS platform, was disrupted in a Microsoft-led partnership – SpyCloud’s data on 8,700+ compromised accounts helped make it happen.
Recaptured data numbers for September 2026
September monthly total
Total New Recaptured Data Records for September:
3,437,557,442
New Cookie, Session Token, and Authentication Access Records:
978,059,823
New third-party breach data this month
Third-Party Breaches Parsed and Ingested:
4,187
New recaptured phished data this month
New Phished Data Records:
27,142,201
New infostealer malware data this month
Stealer Logs Parsed and Ingested:
6,084,305
New Data Records from Stealer Infections:
191,158,278
Discover what cybercriminals know about your business and your customers – and how to prevent targeted attacks with SpyCloud.
Keep reading
During this flurry of activity, law enforcement authorities also arrested two SLSH-affiliated actors; the individual behind the moniker Umbreon was arrested in the Netherlands and Rey was arrested in Jordan. In addition to a host of cybercriminal charges, Pepijn van der Stap – the real person behind Umbreon – is being charged with the attempted incitement of two murders. KrebsOnSecurity reported that van der Stap’s arrest was on September 16, and Reuters reported that Saif al-Din Khader (the real identity of Rey) was arrested on September 29. This means that the brazen public threats, hacking, and hijacking carried out against Cl0p and the FBI occurred in the window between these two arrests.¹
As of the time of this writing, the original SLSH site appears to be offline. There is a new site that is up but so far it is unclear whether this new site is just a clone from cached data run by scammers or if it is indeed SLSH trying to reappear after losing Rey. Currently no new listings of victims have been created and all previous in-process victims have been removed.