

RESOURCE HUB
Malware Intelligence:
Go From Exposure to Enterprise Resilience
Infostealers don’t just steal passwords – they hand attackers a complete identity toolkit to gain initial access and launch attacks. SpyCloud recaptures what malware steals, so you can act before criminals do.

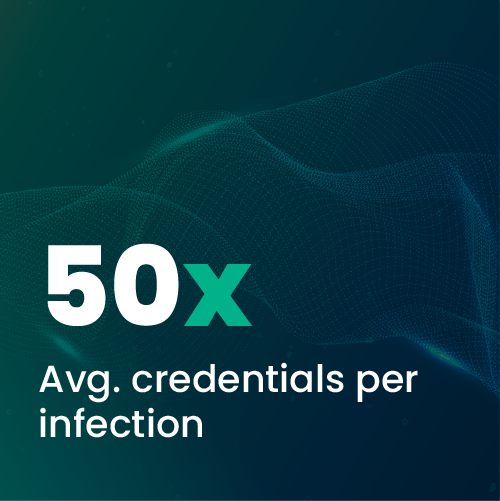
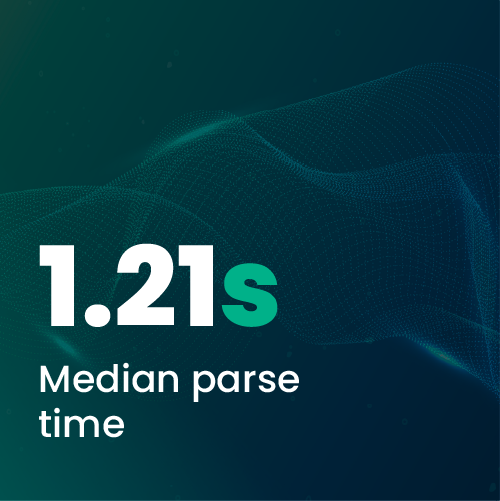
- StealC - Steals cookies
- LummaC2 - Active & Evolving
- Atomic Stealer - Targets macOS
- Vidar - High-Volume Campaigns
- RisePro - Steals Financial Data
THE MALWARE ENTERPRISE THREAT
The reality of enterprise malware risk
False Sense of Security
Traditional defenses aren't stopping infostealers
EDR and antivirus tools are essential – but they don’t defend you fully. Infostealers are specifically engineered to evade detection, execute rapidly, and disappear before endpoint tools can flag them. By the time a scan fires, the data is already in criminal hands.
66%
of malware infections occurred on endpoints already running EDR or antivirus tools according to SpyCloud research
Data Weaponization
A single infection gives criminals a multi-pathway attack kit
Stolen credentials, session cookies, and tokens don’t just unlock one door, they open entire enterprise environments. SpyCloud recaptures this data from the underground before it’s weaponized against your organization.
642.4M+
malware-exfiltrated credentials recaptured last year by SpyCloud
Take Action Now
Post-infection remediation isn't optional – it's urgent
After a malware infection, the clock is ticking. Without immediate remediation of all exposed identities, attackers have everything they need to launch account takeover, commit fraud, or establish persistent access before you’ve even opened the incident ticket.
Malware's role in the modern identity attack chain
Every infostealer infection is the starting gun for a chain of identity-based threats. Here’s how attackers move from device to damage.
Malware Threat Tracking
Top infostealer variants we're tracking
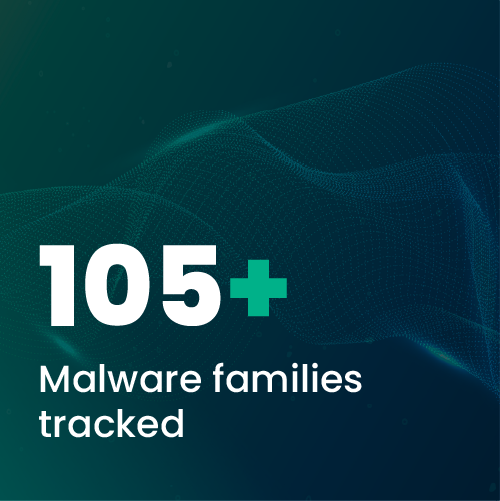
Total malware
families tracked
LummaC2
Most active
A sophisticated, modular infostealer distributed primarily as Malware-as-a-Service. LummaC2 aggressively targets browser sessions, cryptocurrency wallets, and two-factor authentication tokens, making it a top driver of authentication bypass attacks against enterprise environments.
Vidar
High volume
One of the most prolific stealers in circulation, Vidar harvests credentials, autofill data, and browser cookies at scale. Its adaptable architecture allows rapid deployment across phishing campaigns targeting enterprise and consumer users alike.
Infiniti Stealer
Emerging threat
A fast-growing variant with a particular focus on enterprise environments. Infiniti Stealer excels at extracting stored credentials from corporate VPNs and cloud applications, enabling deep initial access to sensitive corporate systems.
Total recaptured
cookies and tokens
SpyCloud's recaptured malware data & intelligence
The depth, speed, and breadth of our intelligence sets us apart. Here’s what our recaptured collection pipeline looks like in practice.
2026 Malware Infection Count
Monthly tracking of new malware infections ingested across our underground collection pipeline – 2026 year to date.
Global Distribution of Infections
Year-to-date infostealer infection activity by global region
Latest infostealer intelligence & analysis
Fresh insights from the SpyCloud research team – curated for you straight from the underground.
Watch SpyCloud on YouTube
ANNUAL REPORT
SpyCloud’s 2026 Identity Exposure Report Highlights the Surging Identity Attack Surface
Uncover the latest identity security threats in the 2026 Identity Exposure Report. Learn how cybercriminals are exploiting stolen data and what you can do to stop them.
THREAT ANALYSIS
Analyzing the Impact of the Operation Endgame Takedown on Rhadamanthys & the MaaS Ecosystem
RESEARCH
Freshly Stolen: The New Age of Combolists
USE CASES
Put our malware intelligence to work
SpyCloud’s recaptured data powers a broad range of security and fraud prevention use cases – all from a reliable source of underground truth. Up-level your defenses with trusted malware intelligence from our platform.
Automate identity exposure remediation
Automatically invalidate stolen sessions, reset compromised credentials, and trigger remediation workflows before attackers can exploit what malware has already stolen.
Prevent authentication bypass
Prevent ransomware
Cut off the initial access pathway. Ransomware operators rely on stolen credentials to establish footholds. SpyCloud intelligence disrupts the attack before it escalates.
Detect insider threats
Identify employees whose devices and credentials have been compromised by malware, enabling rapid response to insider risk driven by external infection.
Remediate supply chain threats
Monitor third-party and vendor exposure. When a supplier’s credentials appear in stealer logs, you’ll know before the threat reaches your environment.
Power Zero Trust policies
Feed real-time compromised identity signals into your Zero Trust architecture to continuously validate access decisions based on actual threat intelligence.
Endpoint Threat Protection
See how malware intelligence is operationalized in our platform – and your workflows
-
Detect infected devices in your environment
SpyCloud matches stolen data to employee identities and corporate domains in real time - Identify all exposed identities automatically Enumerate every stolen credential, cookie, and token tied to the infection
- Trigger automated remediation Invalidate sessions, reset passwords, and feed alerts into your SIEM or SOAR
"SpyCloud gives us visibility into threats that would otherwise be invisible to us – specifically the stolen sessions and credentials that bypass every traditional control we have. It's not just intelligence, it's the remediation capability that makes it operationally valuable."
Fortune 500 Enterprise: Atlassian
See your malware exposure before criminals use it against you
Find out what infostealers have already stolen from your organization — and get a roadmap to remediate it before it becomes a breach.
Malware intelligence FAQs
Malware intelligence is information about malware families, how they spread, and what they steal from infected devices. Traditional threat intel tracks indicators such as file hashes and command-and-control domains. Identity-focused malware intelligence shows what an infection exposed: which session cookies, authentication tokens, and credentials left the device, and which users and applications they unlock. SpyCloud tracks 105+ malware families and recaptures the data they steal.
SpyCloud recaptures data stolen by 105+ malware families from the criminal underground, instead of indexing what is already posted. SpyCloud matches the session cookies, authentication tokens, MFA codes, and credentials in that data to your employees, customers, and suppliers. Endpoint Threat Protection and SpyCloud’s integrations then push password resets and session revocations to identity providers such as Okta and Entra ID.
Ransomware encrypts data, and spyware watches a user over time. An infostealer steals access, so it usually opens an attack rather than finishing it. SpyCloud’s 2024 Malware and Ransomware Defense Report found that nearly one third of companies hit by ransomware had an infostealer infection in the prior 16 weeks.
- Infostealers copy session cookies, authentication tokens, and saved credentials in seconds.
- Remote access trojans (RATs) give attackers ongoing control of a device.
- Banking trojans target financial logins, often on mobile devices.
- Loaders install other malware, often a stealer, after the first infection.
SpyCloud recaptures data from infostealers and from mobile malware such as the ERMAC banking trojan.
Malware that steals data has already copied live session cookies and authentication tokens. Those sessions already passed MFA, and they stay valid until each application revokes them. Reimaging removes the malware but leaves the stolen sessions active, and a password reset does not reliably end existing sessions. Full remediation means:
- listing everything the malware took
- resetting the exposed credentials
- revoking sessions in each affected application and identity provider
- reviewing accesslisting everything the malware took
resetting the exposed credentials
revoking sessions in each affected application and identity provider
reviewing access
Most infections start with phishing emails, malicious ads, fake software installers, or cracked software. Criminal traffer teams get paid to drive victims to malware downloads. Malware-as-a-service operators rent their tools to anyone with a subscription. Many infections land on personal and contractor devices used to reach corporate apps, outside the reach of EDR.
Isolate and clean the device, then pull the full list of what the stealer took. Reset every exposed credential, revoke sessions and refresh tokens in the identity provider and SaaS apps, and check logs for any use of the stolen sessions. Include the user’s personal devices and third-party accounts in the review, since the stealer captured those too.
- listing every session cookie, authentication token, and credential in the stealer log
- resetting the credentials
- revoking the sessions in each affected application and identity provider
- reviewing access
SpyCloud’s 2026 Identity Exposure Report found that 40% of malware infections occurred on devices with EDR or antivirus installed. Many strains run, send stolen data to the attacker, and delete themselves within seconds. Even when an endpoint tool flags the infection, the stolen data is already gone. Infections on unmanaged devices never reach the security team at all.
Malware gives ransomware crews their way in. Stolen credentials and session cookies let attackers sign in to VPNs, remote access tools, and cloud consoles as a legitimate user. SpyCloud’s 2024 Malware and Ransomware Defense Report found that nearly one third of companies hit by ransomware had an infostealer infection in the prior 16 weeks.