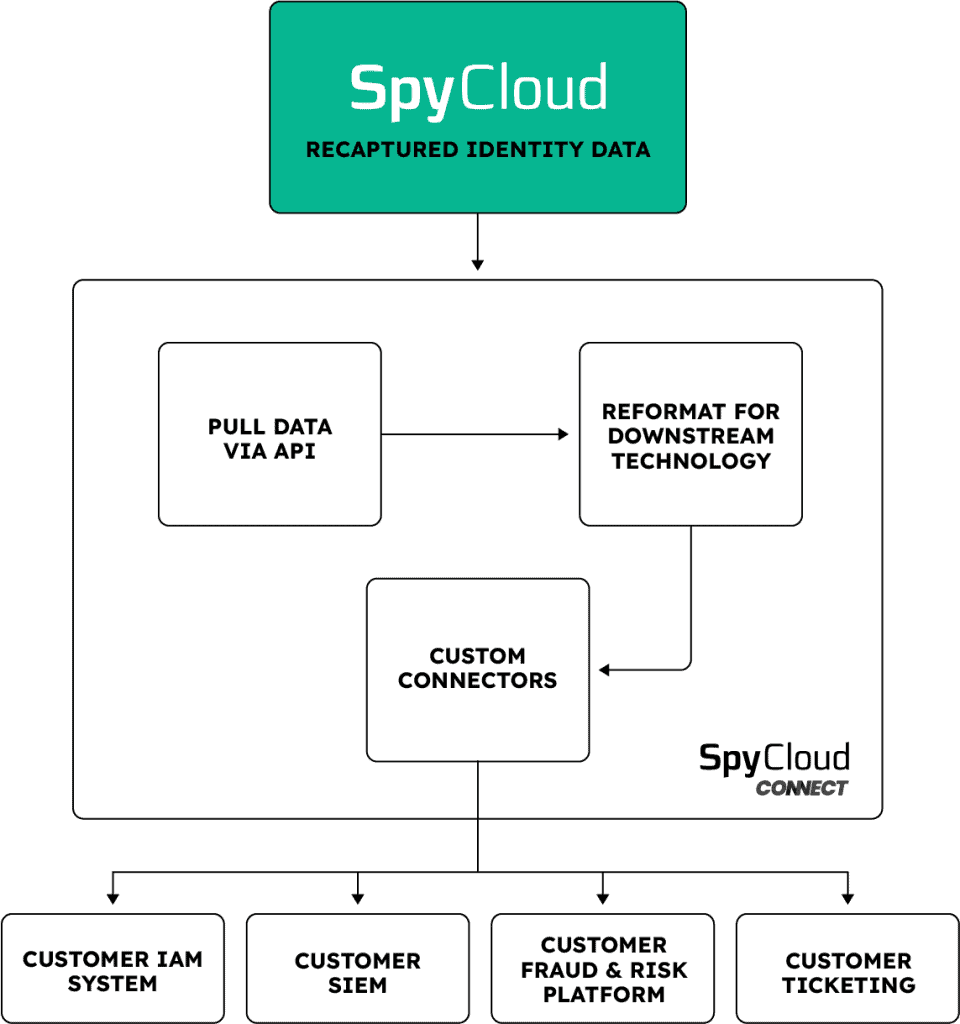
SpyCloud integrates with Splunk, Elastic SIEM, Google Chronicle (Google SecOps), Microsoft Sentinel, and Devo. These integrations deliver SpyCloud’s recaptured breach records, infostealer malware logs, and phishing capture data as enrichment signals, improving event correlation and helping analysts prioritize identity-related alerts. Security teams can correlate SpyCloud exposure data with authentication events, endpoint alerts, and access logs in the same SIEM workflow they already use, without building custom data pipelines.