

Demo Center Home > Workforce Threat Protection Demo
Workforce
Threat Protection
Detect and respond to employees exposed via malware, phishing, and breaches before attackers can act.
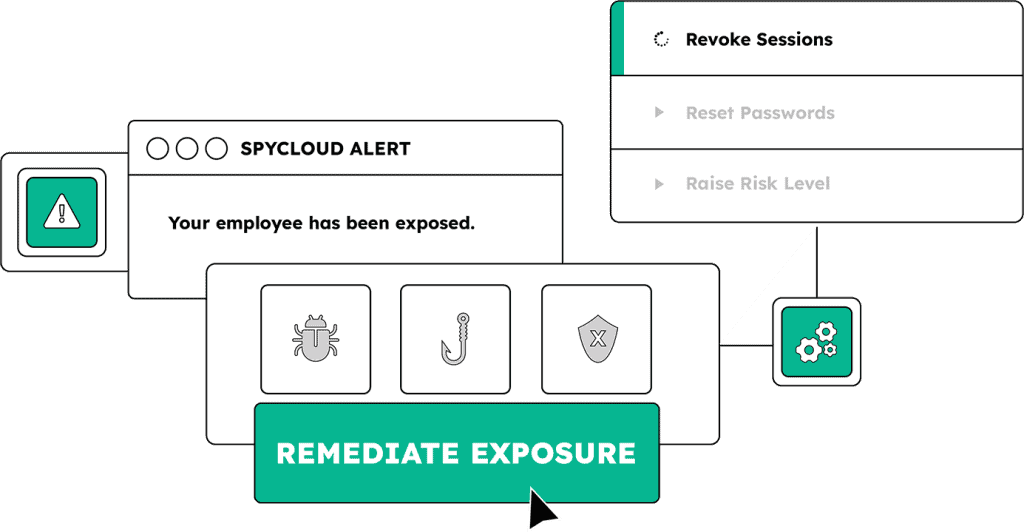
Walk through detection to remediation of an exposed workforce identity,
using recaptured breach, malware, and phishing data.
What you'll see
From confirmed exposure to automated response
SpyCloud Workforce Threat Protection detects when an employee’s corporate identity has been exposed through a data breach, a malware infection, or a successful phishing attack, and it triggers remediation before that exposure can be used for account takeover, session hijacking, or other identity attacks.
SpyCloud recaptures this identity data from the criminal underground rather than only scanning public sources, which is why an exposure often appears in SpyCloud before it is ever used against you.
This demo walks through how a security team surfaces exposed workforce credentials, sees the full context of each exposure, and applies an automated response such as a password reset or a forced re-authentication within their existing security stack. It shows how that data maps to the real identities in your workforce so you can act on confirmed exposures instead of generic alerts.
Surface
Inspect
Match
Remediate
Confirm
Outcomes of
Workforce Threat Protection
What the data behind this demo shows
80%
65.7B+
56%
HOW IT WORKS
Recapture, match, deliver, respond
STEP 1
Recapture
Pull exposed identity data straight from the criminal underground, so an attack surfaces before an attacker can use it.
STEP 2
Match
Continuously check your identities, including reused credentials, against recaptured data to confirm real exposures.
STEP 3
Contextualize
Surface the source and the specific data exposed, so responders act on a confirmed exposure instead of a generic alert.
STEP 4
Remediate
Trigger a password reset or force full re-authentication through your existing identity provider to start a scheduled response.
CHOOSE YOUR FIT
Corporate logins are only half the risk
Most tools check the corporate email and stop there. Attackers do not. Workforce Threat Protection matches the full identity, surfacing the reused personal credentials and session data tied to the same employee.
What most tools check
- work@company.com
One identifier.
The exposures tied to everything else stay invisible.
What SpyCloud matches
- work@company.com
- personal@gmail.com
- reused username
- reused password
- session cookie
Check Your Exposure
See what recaptured criminal underground data already ties to your workforce. Check Your Exposure for a fast read on your identity risk.
Workforce Threat Protection Demo FAQs
The demo shows how SpyCloud detects an exposed employee identity, presents the exposure details and its source, and applies an automated remediation such as a password reset or session revocation through your identity provider. It is a guided walkthrough of the detection-to-remediation workflow using recaptured identity data.
Most dark web monitoring tools alert you that a credential appeared somewhere and stop there. SpyCloud recaptures the underlying identity data from the criminal underground, matches it to your actual workforce accounts, and enables automated remediation, so you can act on a confirmed exposure rather than triage an alert.
A password reset invalidates a stolen password, but it does not revoke an active session. If malware also stole a valid session cookie or authentication token, an attacker can continue to access the account after the reset by replaying that session and bypassing MFA. Full remediation requires resetting the credential and terminating the exposed session, which is why SpyCloud pairs credential remediation with session-level detection.
It detects exposures from third-party data breaches, credential-stealing malware infections, and successful phishing attacks, including exposures tied to an employee’s personal accounts where those credentials overlap with corporate access.