

Demo Center Home > Holistic Identity Demo
See how one exposed asset expands into a person’s full risk picture, and how SpyCloud remediates the entire exposure automatically. Walk through how one exposed credential expands into a full holistic identity with IDLink, then gets remediated automatically across Active Directory, Entra ID, and Okta.
HOLISTIC IDENTITY Protection by SpyCloud
This demo follows a single identity end to end, from one recaptured credential to the full set of exposed assets connected to that person, and finally to automated remediation. You will see how SpyCloud surfaces an exposure, expands it into a holistic identity view with IDLink, and closes the access without an analyst chasing it down.
The walkthrough moves from detection to full remediation. SpyCloud confirms an exposed identity, IDLink maps everything tied to that person, and Identity Guardians reset the exposed password and revoke active sessions according to your policy, whether the environment runs on Active Directory, Microsoft Entra ID, Okta Workforce Identity, or a combination of them.
Same holistic identity, same automatic response across Active Directory, Entra ID, and Okta, whether your workforce identities are on-prem, hybrid, or fully cloud.
A recaptured phishing record, matched to a real exposed employee and flagged HIGH severity on a confirmed email and plaintext password.
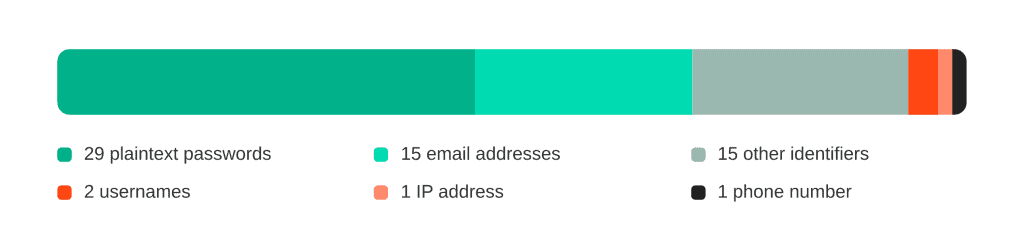
IDLink pivots across the full dataset, turning one email into 63 connected identity assets, 61 of which exact matching would never surface.
The graph maps every reused email, username, and password back to one employee, so you act on the whole identity instead of a single login.
Identity Guardians reset the exposed password and revoke active sessions across Active Directory, Entra ID, and Okta, no analyst required.
The demo starts with a single email address. IDLink expands it into 63 exposed identity assets tied to the same person,
and 61 of them surface only because of IDLink.
See your organization’s real exposure,
matched against SpyCloud’s recaptured identity records.
It shows how SpyCloud turns a single exposed credential into the full holistic identity behind it, then remediates that exposure automatically. The walkthrough moves from one recaptured phishing record tied to an employee, through an IDLink search in SpyCloud Investigations that surfaces 63 connected identity assets, to an automated password reset through Active Directory Guardian.
A holistic identity is the complete set of data tied to one person across their online life: work and personal emails, usernames, current and historical passwords, PII, financial data, and location. Attackers assemble these fragments to bypass single-account defenses, so remediating one credential in isolation leaves the rest of the identity exposed. SpyCloud maps the whole identity so a team can act on all of it.
IDLink is SpyCloud’s identity analytics capability for pivoting across recaptured data. It correlates the many fragments that make up a person’s identity, such as emails, usernames, and passwords reused across accounts, to connect exposures an exact credential match would never link. In the demo, exact matching would have found a handful of assets, while IDLink surfaces 61 additional ones, and across a workforce it finds up to 14x more exposed plaintext passwords per user.
The data is recaptured from the criminal underground, including third-party breaches, infostealer malware records, and successfully phished data. Because SpyCloud recaptures it close to the source rather than scraping public sites, exposures often appear before criminals have used them, which gives defenders time to remediate.
SpyCloud’s Identity Guardians act on confirmed exposures without analyst effort. Active Directory Guardian scans AD accounts against recaptured data and can reset an exposed password within five minutes of discovery, forcing a change at next login. Equivalent solutions extend the same automated detection and remediation to Entra ID and Okta, so the exposure is closed wherever your workforce authenticates.
NEW RESEARCH: Over 2/3 of orgs had an identity event last year – NHIs were the top cause. Read on →